
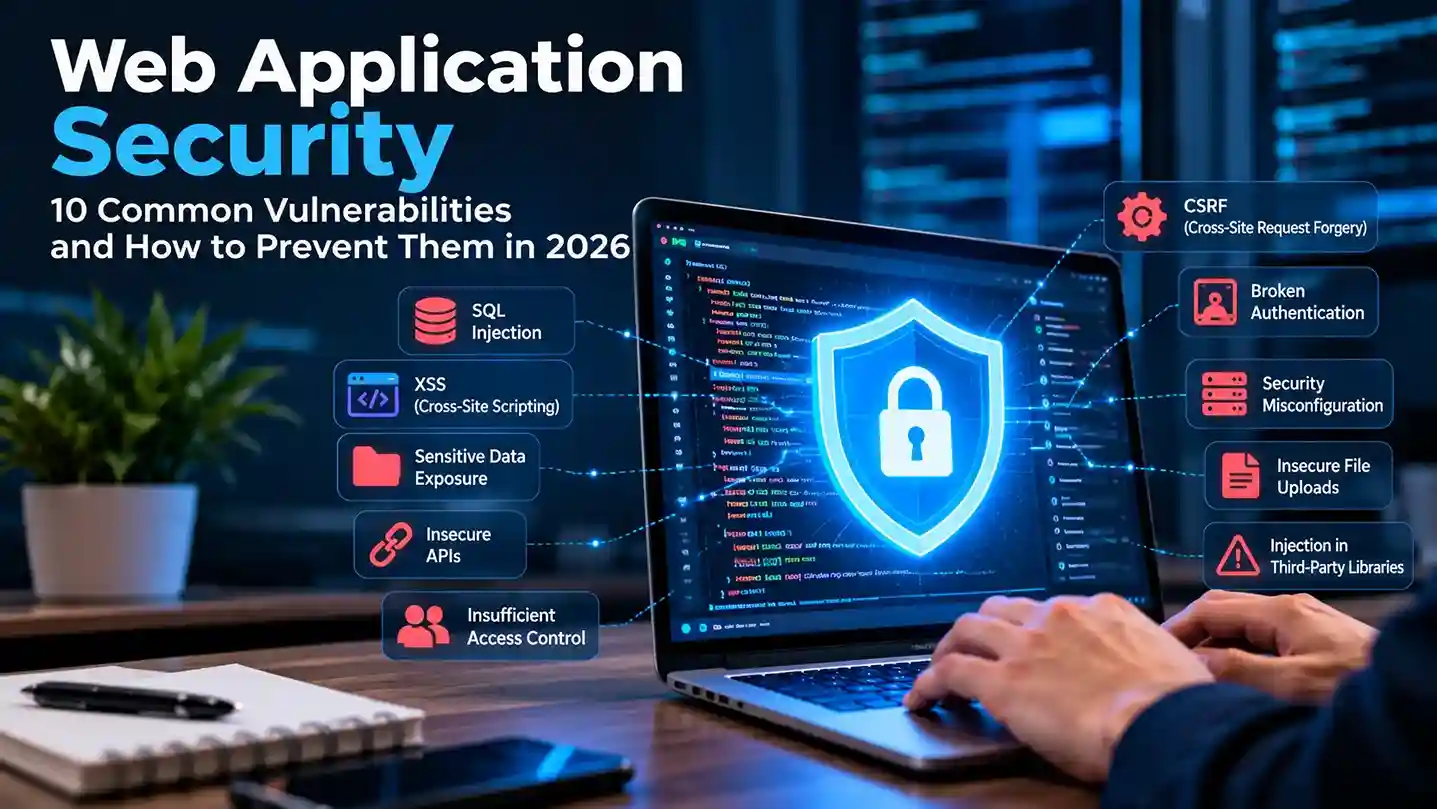
A web application can look polished and still expose customer information, account access, or business operations through a security flaw. These risks are not limited to large platforms. Small business websites, custom PHP systems, and ecommerce dashboards can be affected too.
This guide explains ten common web application vulnerabilities, what they mean in practice, and the steps development teams can take to reduce risk. It is a practical starting point, not a substitute for a professional security assessment.
SQL injection happens when untrusted input changes the meaning of a database query. It can expose or modify records when an application constructs SQL by joining user input into a query.
Use parameterized queries and prepared statements for every variable input. Give database accounts only the permissions they need, and test search, login, and filtering endpoints.
Cross-site scripting occurs when attacker-controlled content is rendered as executable code in another visitor’s browser. Comment fields, search results, and profile data are common places to check.
Escape output for its HTML, attribute, URL, or JavaScript context. Sanitize rich text with a trusted library and consider a carefully configured Content Security Policy.
CSRF can trick a logged-in browser into sending an unwanted action, such as changing account settings, if the application does not verify the request.
Protect state-changing requests with CSRF tokens, suitable SameSite cookie settings, and checks for sensitive operations. Never rely on a hidden form field alone as authorization.
A user may be able to access another person’s order, invoice, or administrative function by changing an ID or requesting an unprotected URL.
Check authorization on the server for every sensitive action and object. Test roles and ownership, including direct requests that bypass the visible interface.
Predictable login flows, reused sessions, or poorly protected cookies make account takeover easier. Password reset endpoints are part of the same attack surface.
Use strong password hashing, rate limiting, multifactor authentication where appropriate, secure and HttpOnly cookies, session rotation after login, and expiring reset tokens.
Debug output, exposed backup files, default accounts, and permissive server settings can disclose information or create easy entry points.
Disable production debug displays, remove unused services, restrict file access, configure security headers, and review deployment settings before launch.
Applications often depend on packages, plugins, frameworks, and libraries. Known vulnerabilities in these dependencies can put the entire site at risk.
Maintain an inventory of dependencies, monitor security advisories, patch supported versions promptly, and test updates in staging before deployment.
An upload feature may accept executable scripts, oversized files, or misleading file types if validation is weak.
Allow only necessary file types, validate content on the server, generate safe filenames, impose size limits, and store uploads outside executable paths where possible.
Personal information and credentials can leak through insecure transport, logs, backups, or incorrectly configured storage.
Use HTTPS, encrypt sensitive information where needed, avoid logging secrets, manage encryption keys separately, and retain only data the business actually requires.
SSRF occurs when a server fetches a URL supplied by a user and can be tricked into reaching internal services or metadata endpoints.
Restrict outbound destinations, validate URLs and redirects, block internal network ranges, and avoid unrestricted URL fetching in import or preview features.
Review access controls, test forms and APIs, scan dependencies, confirm backups and recovery procedures, enable monitoring, and run security testing appropriate to the application.
For a PHP or WordPress project, security should continue after launch through updates, logging, incident response planning, and periodic reviews.
Secure development is a process, not a one-time plugin installation. The most effective approach combines careful coding, sensible server configuration, regular updates, and real testing.
If your business needs a custom application or a security-focused website upgrade, Alien Web Solutions can help plan the development and review process.
There is no single mistake across all applications. Broken access control, injection, weak authentication, and misconfiguration are important risks to assess.
Prepared statements are a core defense for variable query values, but secure database permissions and validation are still important.
Yes. Automated scans and attacks can affect websites of any size, so basic security controls matter even for small businesses.
Test before major releases and after meaningful changes, and schedule periodic reviews based on the application’s risk and sensitivity.
No. HTTPS protects data in transit but does not fix vulnerabilities such as broken authorization, XSS, or insecure file uploads.
